HIPAA-Compliant Contact Forms for Medical Websites: What Practices Need to Know
A standard website contact form can expose patient information. Here is what to check before your practice collects health details online.
DevGlim Team
October 24, 2026
Looking to build this instead of buying it? See our Healthcare Website Design & Development Services service →
Most medical websites have a contact or appointment request form. Many of them were set up with the same plugin a restaurant might use, sending each submission as a plain email. If patients describe symptoms, conditions or medications in that form, the practice may be handling protected health information (PHI) in a way it has not assessed. This guide explains the main points to review. It is general information, not legal advice; confirm your obligations with your compliance officer or counsel.
When does HIPAA apply to a website form?
HIPAA applies to covered entities, such as most healthcare providers that bill insurance electronically, and to their business associates. Information becomes PHI when health information is linked to an identifiable person. A form that collects a name, contact details and a reason for the visit can therefore create PHI as soon as it is submitted. A general "ask us a question" form may still receive health details because patients type them in anyway.
Six things to check
1. A Business Associate Agreement with every vendor that touches the data
If a form provider, hosting company, email service or CRM stores or transmits PHI on your behalf, it is generally acting as a business associate and needs a signed Business Associate Agreement (BAA). Many popular form builders offer a BAA only on specific plans, and some do not offer one at all. Check before you collect anything sensitive.
2. Encryption in transit and at rest
The page must load over HTTPS, and stored submissions should be encrypted. Ask the vendor where data is stored, how it is encrypted and how long it is kept.
3. Do not send submission contents by ordinary email
The common setup, where the form emails the full submission to a front-desk inbox, is the weakest link. A safer pattern is to send a notification only ("a new request is waiting") and have staff log in to a secure portal or practice system to read it.
4. Tracking pixels and analytics on form pages
Advertising pixels and some analytics scripts can send page URLs, form events or entered values to third parties. The U.S. Department of Health and Human Services has issued guidance on tracking technologies on healthcare websites, and parts of that guidance have been challenged in court, so the position may change. The practical step is the same either way: audit which scripts run on appointment and form pages, and remove or configure any that could transmit health information without an appropriate agreement.
5. Collect only what you need
A first-contact form rarely needs a diagnosis, date of birth or insurance number. Ask for a name, preferred contact method and a general reason ("new patient appointment", "billing question"), and gather clinical details later through the patient portal or at intake.
6. Access control and audit logs
Only staff who need submissions should be able to see them, each with their own login. The system should record who viewed or exported a record, and submissions should be deleted or moved into the patient record on a defined schedule.
Options for a safer setup
- A HIPAA-eligible form service with a signed BAA, secure inbox and notification-only emails. Quick to set up for small practices.
- Your practice management or EHR system's own request form, embedded on the website, so data goes straight into a system already covered by your agreements.
- A custom form and secure portal, built and hosted under a BAA, when you need integration with scheduling, routing to multiple locations or a specific intake workflow.
Write clear patient-facing wording
Add a short notice next to the form: what the form is for, that it should not be used for emergencies, and, if it is a general enquiry form, that patients should not include detailed medical information. Clear wording reduces risk and sets expectations.
A quick review checklist
- List every form on the site and what each one collects.
- Confirm a BAA exists with each vendor that stores or transmits submissions.
- Switch email notifications to "notification only".
- Audit scripts and pixels on form and appointment pages.
- Remove fields you do not need at first contact.
- Check user access, logging and retention settings.
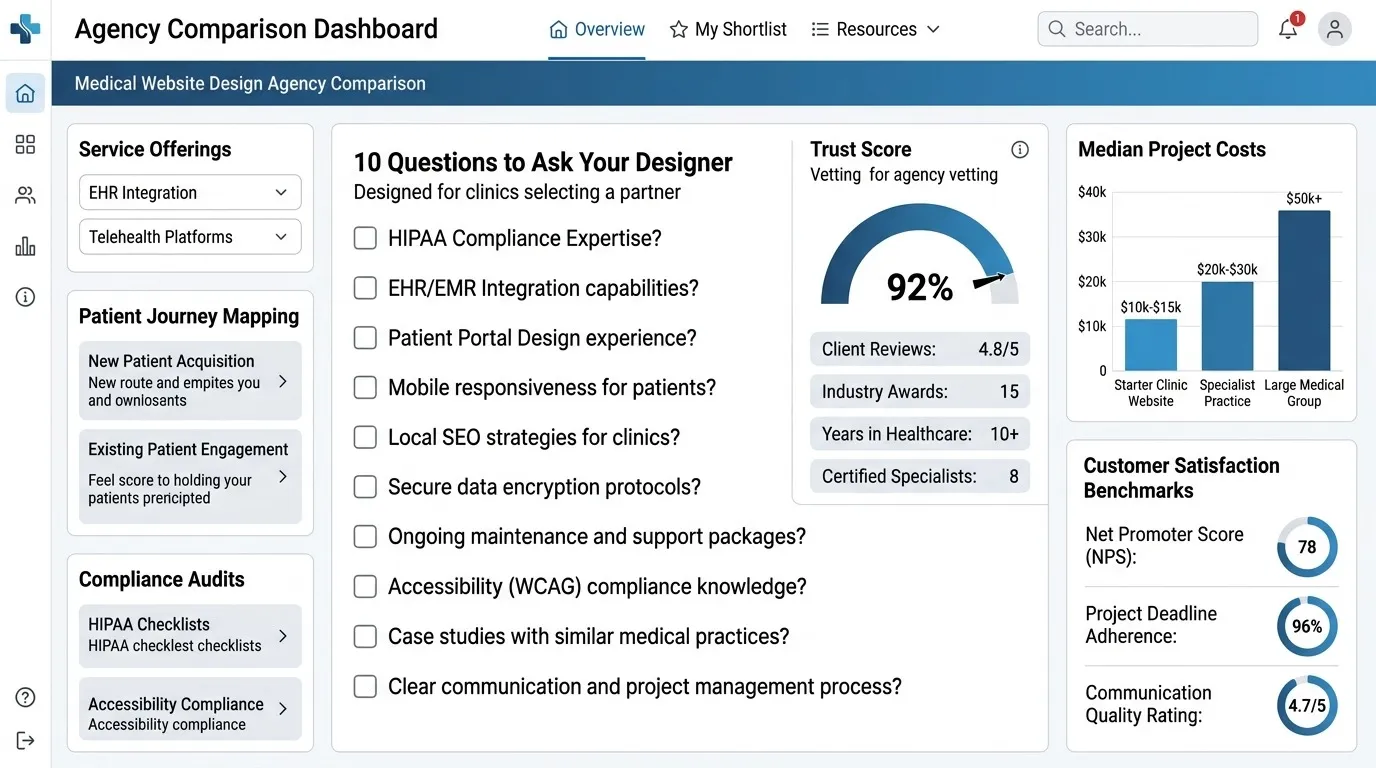
If you are planning a new practice website or redesign, our guide on choosing a medical website design company covers what to ask vendors. DevGlim's healthcare web team can review your current forms and tracking setup or build a secure intake flow.